IT Fabric · Security Operations
Microsoft 365, Identity and Security Operations
Bring identity, Microsoft 365, endpoint, vulnerability, infrastructure, network, and change evidence into one investigation and route consequential response through the right controls.
Find risk earlier. Respond with context.
What improves
- Turn isolated security signals into a more complete investigation.
- Find identity and Microsoft 365 compromise evidence earlier.
- Give frontline technicians useful security context without granting unrestricted administrative access.
Supported behavior
Microsoft 365 and identity security
Risky sign-ins, impossible travel, password spray, privileged changes, and credential exposure, tied to the person and the device involved, where supported.
Active Directory intelligence
Authentication behavior, privileged change, service accounts, and lateral-movement signals, correlated instead of listed.
Credential exposure monitoring
Approved breach intelligence surfaces exposed credentials before someone else uses them.
Network and DNS context
Anomaly and change context seen against the topology and the services on it.
Vulnerability intelligence
Findings reconciled with endpoint and patch truth where supported, so the list you act on reflects what is actually exposed.
Zero-trust network access
Identity-aware access to applications and services instead of broad network reach, so a compromised credential meets a policy boundary, not a flat network, delivered through supported ZTNA integration and scope.
Governed containment
Contain a user, device, access path, or service through an approval-aware workflow, with a record of who said yes.
In practice
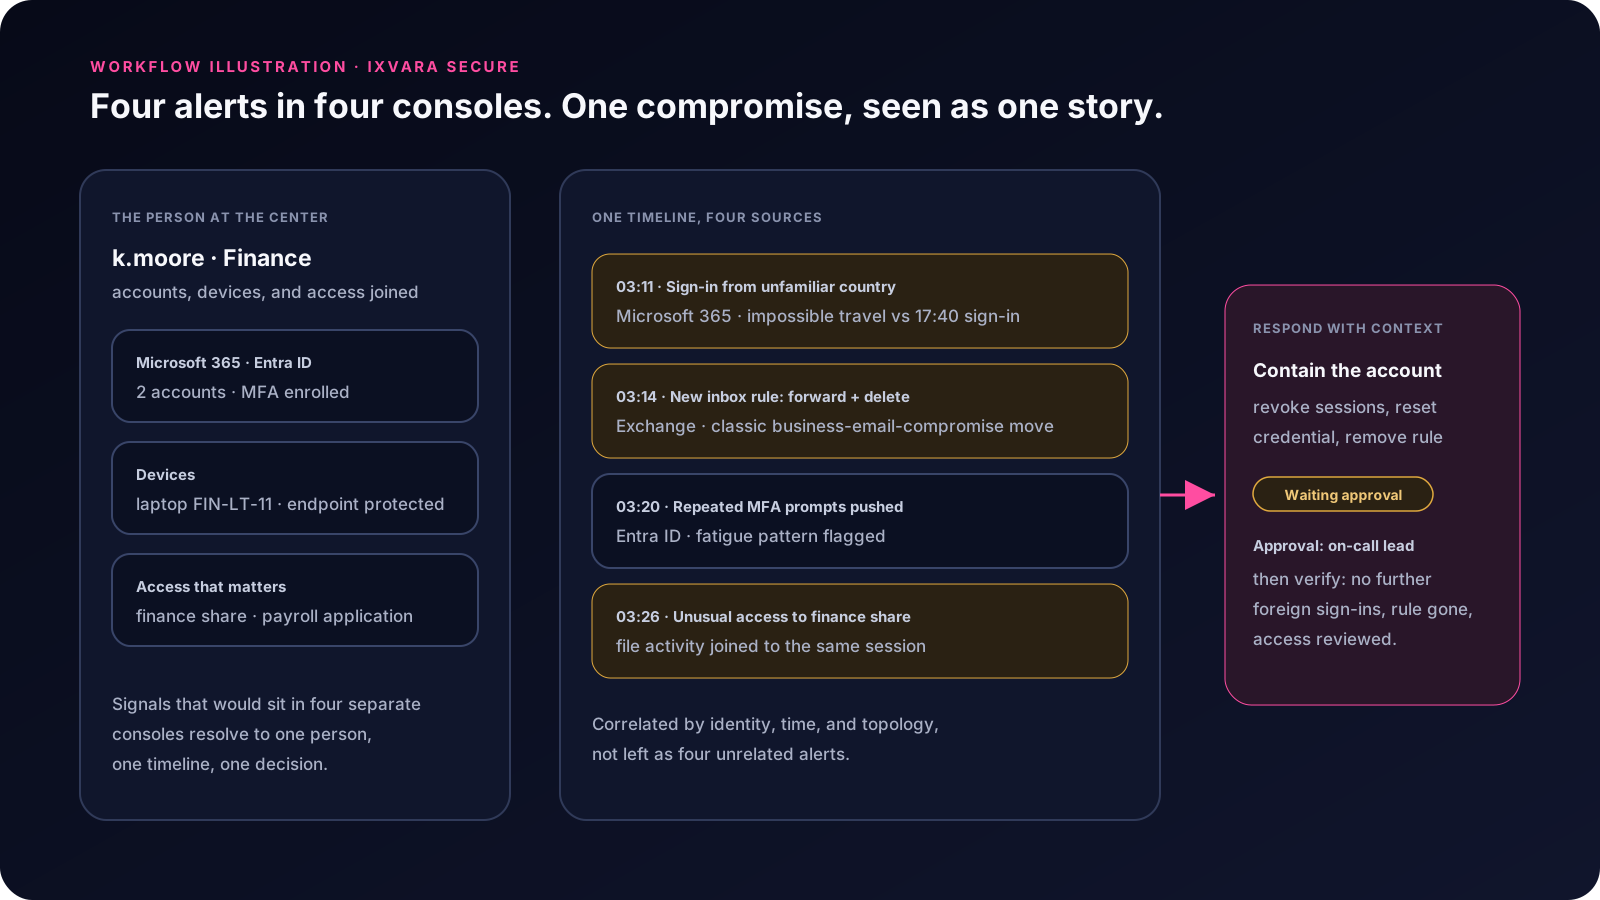
One sign-in from the wrong country. Three systems that each saw part of it.
Microsoft 365 flags a risky sign-in. The firewall logged the session. The endpoint shows a patch gap. Ixvara Secure puts the three together, names the person, their devices, and the access they hold, and proposes the containment sequence. You approve it, and the record shows who did.
Connected to the rest of the fabric
Security Operations shares operating context, governance, and outcome history with every other IT Fabric domain. The evidence gathered here strengthens investigations everywhere else.
See this on a workflow that matters to you.
Tell us where the effort goes today. We will build the demonstration around that workflow.