Trust and Governance
AI Governance and Human Approval Controls
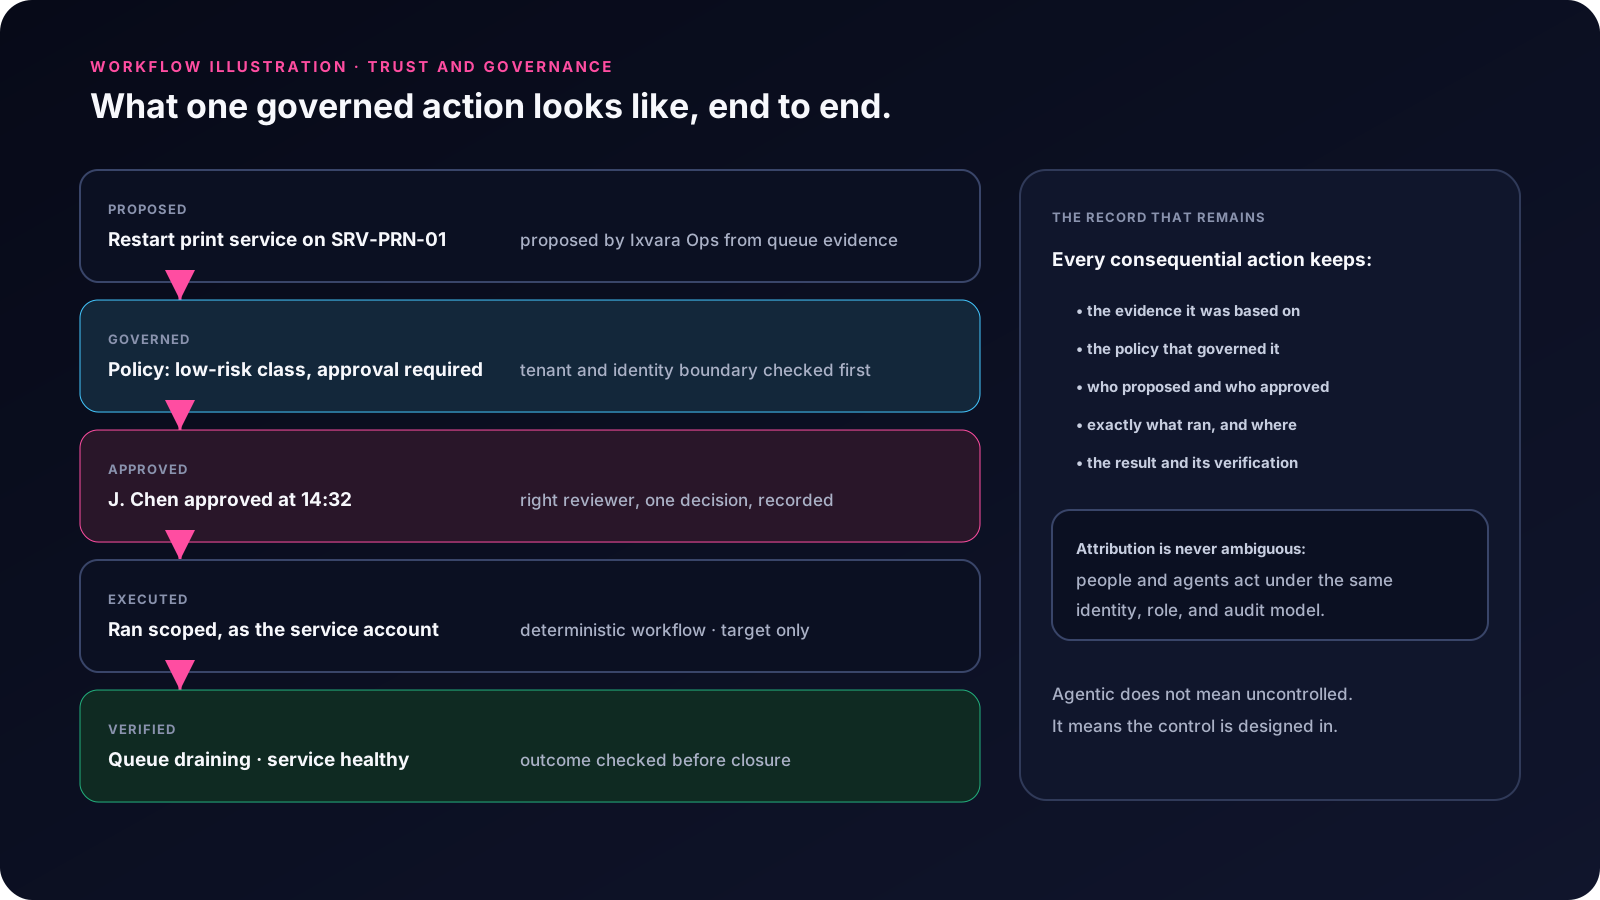
Agentic does not mean uncontrolled. Ixvara is designed to increase operating speed while preserving human authority, tenant isolation, least privilege, policy, approval, auditability, and verification.
Governance Controls
Tenant and identity boundaries
Every query and action is scoped to the authorized organization and principal.
Role and policy controls
People and agents receive only the authority required for the task.
Human approval
Consequential actions can pause for the correct reviewer, with step-up verification including multi-factor confirmation for sensitive approvals.
Stronger authentication for destructive action
Supported destructive operations require multi-factor confirmation and leave an audit record.
Audit and attribution
Evidence, decision, actor, action, and result are preserved.
Verification
The supported outcome is checked before the loop closes.
Data and model placement
Cloud, Hybrid, and Private deployment choices, with explicit local-only behavior and no silent cloud fallback in local-only policy mode.
Outbound local connectivity
Collectors and appliances connect outbound where supported, so routine collection needs no inbound firewall rules.
Prompt-injection and untrusted data
Agentic workflows and Ixvara IQ treat retrieved and user-supplied content as data, not instructions, and consequential action still requires policy and approval.
Observational access
Discovery and observation are approved, scoped, purpose-specific, role-aware, and auditable: limited to the systems and information the engagement requires, never unrestricted monitoring of users.
Compliance support
Ixvara technology supports control objectives. It does not by itself constitute certification, and no certification is claimed without evidence.
Audit Logging and Action Verification
Bring your security team.
Identity, approvals, audit, collectors, and deployment, answered directly against your requirements.